Secrets
Skiff 2 uses Google Secret Manager to store sensitive information such as API keys, database credentials, and service tokens.
Creating Secrets
- Open Google Secret Manager for your project.
- Verify you've selected the correct Google Project by checking the project name at the top of the page.
- Click "Create Secret".
Naming Format
Secret names must follow a specific format so they are automatically mapped to the correct service and environment:
<ENV_NAME>-<SERVICE_NAME>-<ENV_VARIABLE_NAME>
For example:
prod-api-API_KEY
| Segment | Description |
|---|---|
ENV_NAME | The environment you want to use the secret in. Default is prod. Use global to apply the secret to all environments. |
SERVICE_NAME | The name of the service that will use the secret. Must match the service name in your skiff2.json. |
ENV_VARIABLE_NAME | The environment variable name set in your service. Must be all uppercase with underscores (e.g., DATABASE_URL). |
- Leave all other options as defaults.
- Click the blue "Create Secret" button.
Once created, the secret will be available as an environment variable the next time your service is deployed.
Redeploying your service
If you want to redeploy your service without GitHub build + deploy, you can do so by either:
In your project in Google Cloud Console, navigate to Cloud Run > Service > and then the service you want to redeploy. And click the Edit & deploy new revision button.
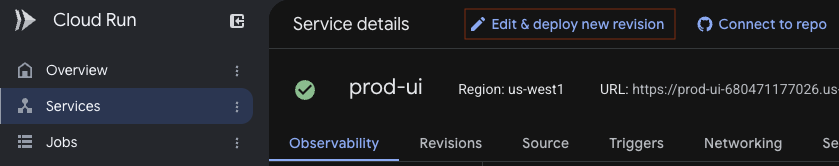
You can leave everything as is, and click the "Deploy" button at the bottom of the page to redeploy the service.
If you want to redeploy from the command line, you can run this command:
# PROJECT should include "ai2-skiff2-" prefix, e.g. "ai2-skiff2-example-app"
# SERVICE_NAME is the name of the service you want to redeploy likley env-service name, e.g. "prod-api"
# REGION is most likely us-west1
gcloud run services update "${SERVICE_NAME}" \
    --project="${PROJECT}" \
    --region="${REGION}" \
    --update-labels="redeploy=$(date +%Y%m%d-%H%M%S)"
Sharing secrets across environments
Secrets are scoped to a single environment by their ENV_NAME prefix. A secret named prod-api-API_KEY will not be picked up by a qa or ad hoc environment.
To share a secret across every environment (including ad hoc environments), use global as the ENV_NAME:
global-api-API_KEY
If both a global- and an environment-specific secret exist for the same service and variable, the environment-specific one wins.
Mounting Secrets as Files
If you need to mount a secret as a file instead of an environment variable, add the secretFiles field to your service in skiff2.json:
{
    "services": [
        {
            "name": "api",
            "secretFiles": {
                "API_KEY": "/path/on/disk/filename.txt"
            }
        }
    ]
}
- The key is the
ENV_VARIABLE_NAMEof the secret you created in Secret Manager. - The value is the file path where the secret will be written inside your container.
Your application can then read the secret by reading from that file path at runtime.
Mounted secret files always track the latest version of the secret in Secret Manager. Creating a new version of the secret will automatically be reflected in the file contents.
There is a performance cost associated with reading from a mounted secret file per request, rather than using an environment variable, and it is recommended to use environment variables for this reason.